What Is AI-SDLC? How AI Reshapes Every SDLC Phase in 2027
Most development teams now use AI to write code. Far fewer have changed the way they plan, test, review, and release software to match, which is why so many AI pilots feel fast but still miss deadlines.
What is AI-SDLC? It is the software development life cycle with AI working in every phase, not only coding, while people stay accountable for each decision. This guide explains what changes in each phase, where AI creates new bottlenecks, and which practices keep quality and security on track. It also includes a short readiness check you can run with your team this week.
Key Takeaways
- AI-SDLC keeps the familiar SDLC phases but builds AI into each one, with people reviewing and approving the output.
- Teams usually move through three levels: AI-assisted, AI-driven, and agentic.
- Faster coding moves the bottleneck to code review, testing, and requirements.
- AI-generated code needs the same security scanning and review as any unreviewed code.
- The biggest gains come from fixing delivery foundations first, then applying AI across several phases.
What Is AI-SDLC?
AI-SDLC is the software development life cycle with AI built into every phase, from gathering requirements to maintaining code in production, while engineers stay accountable for every decision. The phases stay the same. What changes is who produces the first draft of the work: AI drafts the requirements, code, and tests, and people review, correct, and approve them.
That is the plain AI SDLC meaning. Adopting it is mainly a question of roles: deciding who drafts, who reviews, and who signs off at each step.
AI-SDLC vs. Traditional SDLC
In a traditional SDLC, people produce every artifact by hand. In AI-SDLC, AI produces the first version and people judge whether it is right.
| Aspect | Traditional SDLC | AI-SDLC |
|---|---|---|
| Requirements | Analysts write user stories after meetings | AI drafts stories and flags gaps; analysts confirm them |
| Coding | Developers write most code by hand | AI drafts code; developers review and refine it |
| Testing | QA writes test cases manually | AI generates tests from requirements; QA checks coverage |
| Code review | Reviewers check human-written changes | Reviewers check larger, AI-assisted changes |
| Deployment | Scripts and checklists gate releases | AI flags risky releases based on past incidents |
| Team focus | Producing the work | Specifying and verifying the work |
AI-Assisted, AI-Driven, and Agentic SDLC: Three Levels of Adoption
Most teams move through three levels, and knowing where you stand tells you what to fix next.
- AI-assisted level: Individual developers use code completion and chat tools. The delivery process itself does not change.
- AI-driven SDLC level: AI is part of several phases, such as test generation, automated review, and incident triage. The workflow is redesigned around it, with review gates and shared project context.
- Agentic level: AI agents take a ticket, write the code, run the tests, and open a pull request. Humans set the goal and approve the result.
Many teams that describe themselves as AI-driven are still at the first level. Everyone has a coding assistant, but nothing else in delivery has changed. Gartner’s research on agentic AI in the SDLC makes the same point: the larger gains come from applying AI across several stages, not only to writing code.
How Does AI Work in Each Phase of the SDLC?
AI in the SDLC works the same way in every phase: AI drafts the work, and people review and approve it. Below is what that looks like across the six phases: planning, design, development, testing, deployment, and maintenance.
Planning and Requirements
Most projects start with messy input: meeting notes, client emails, and support tickets. AI turns that into draft user stories with acceptance criteria, and it also catches what people miss. Take a story like “users can export reports”: an AI review would ask which file formats, how large a report can be, and who has permission to export.
Answering those questions before development starts is cheaper than fixing them after release. What AI cannot do is decide what matters most. Setting priorities, weighing trade-offs, and agreeing on scope with stakeholders stay with the product owner.
Design and Architecture
Once requirements are approved, AI can draft the first version of the technical design, including API contracts, data models, and architecture diagrams. It can also check a proposed design against your team’s existing standards. For example, it can flag a new service that skips the company’s standard authentication pattern, or a database schema that will struggle once data volume grows.
The final call still belongs to the architect. AI does not know your budget, your compliance obligations, or which systems the client plans to retire next year. Those constraints shape most architecture decisions, and getting them wrong costs far more than any time AI saves on drafting.
Development
Development is where AI is most visible. Developers use it to generate code, refactor old functions, write documentation, and explain unfamiliar parts of a codebase. Coding agents go a step further: given a well-written ticket, they can write the change, run the tests, and open a pull request for review.
The quality of that output depends on the context the AI receives. An agent that can read your coding standards, architecture notes, and existing code produces work that fits the codebase. An agent working from a one-line prompt produces code that runs but has to be rewritten. Developers remain responsible for the logic and for maintaining the code long after it ships.
Testing and QA
AI writes unit tests, generates realistic test data, and suggests edge cases a tester might skip, such as empty fields, unusual characters, or two users editing the same record at once. It also helps track down flaky tests by spotting patterns in failed runs.
There is one trap to watch for. When AI generates tests by reading the code itself, the tests check that the code does what it already does, including its bugs. Good tests come from the requirements, not the implementation. QA engineers stay responsible for deciding what needs testing and whether the test suite actually covers the risks that matter.
Deployment and Release
Many failed releases trace back to small configuration mistakes, and that is where AI helps first. It reviews pipeline and infrastructure files before they reach production, catching problems such as a missing environment variable or an overly broad access permission. It can also compare a new release with past incidents and flag changes that look risky, like a large database migration scheduled during peak hours.
The go/no-go decision stays with people. A release manager weighs things AI cannot see, such as a client demo scheduled for the next morning or a support team that is already short-staffed. AI gives the team a clearer view of the risk, and it can draft the release notes, but it should not approve the release.
Maintenance and Monitoring
An on-call engineer woken at 2 a.m. by forty alerts does not need forty alerts. They need to know what broke. AI groups related alerts into a single incident, points to the likely root cause, such as a recent deployment or a slow database query, and can draft a fix for problems the team has seen before.
AI also makes old code easier to live with. It can explain legacy modules nobody on the current team wrote, generate missing documentation, and suggest a safe order for modernizing them. Engineers still decide which fixes reach production and when a legacy system is worth rebuilding rather than patching.
Where AI-SDLC Breaks: The Bottleneck Moves Downstream
AI does not speed up the whole SDLC evenly. It makes writing code faster, and the pressure moves to the steps after it. A team that adds a coding assistant and changes nothing else usually finds that features are written faster but don’t ship much sooner. The work is still there, waiting somewhere else.
The 2025 DORA report from Google shows this pattern at scale. It found that AI adoption is linked to higher delivery throughput but also to more instability, meaning more failed changes and more rework. Its conclusion is that AI acts as an amplifier: it strengthens teams with solid processes and magnifies the problems of teams without them.
In practice, the pressure lands in three places:
- Code review: developers open more and larger pull requests, so reviewers either become the bottleneck or start approving code they haven’t fully read.
- Testing: a weak test suite used to let a few bugs through. Now it lets bugs through at the speed AI writes code.
- Requirements: a vague ticket used to waste a developer’s afternoon. Now an AI agent can turn it into a thousand lines of confident, wrong code in minutes.
The lesson is to fix what sits downstream before adding more generation upstream. Teams that get real gains from AI-SDLC strengthen review capacity, test coverage, and requirements first, and then let AI speed up what those foundations can support.
AI-SDLC Best Practices in 2027
Here is how teams that get real results from AI-SDLC in 2027 put that lesson into practice. These seven habits cover where to start, what to control, and how to measure progress.
Start With One Bottleneck, Not One Tool
Many teams adopt AI by rolling out a coding assistant to everyone and hoping delivery speeds up. It rarely works that way, because the tool lands wherever it lands, not where the team is actually stuck.
A better starting point is your own delivery data. Look at where work waits longest. If pull requests sit in review for days, an AI review assistant pays off first. If bugs keep reaching production, start with AI-generated tests. Solve one bottleneck, measure the change over a few sprints, then pick the next.
Write an AI Usage Policy Before Scaling
When every developer picks their own AI tools, nobody knows where the company’s code and data are going. One engineer pastes a client’s database schema into a free chatbot; another installs a coding plugin nobody has checked. Problems like these usually surface during a security audit or a client question, when they are hardest to fix.
A usage policy doesn’t need to be long. One page that answers four questions is enough to start: which tools are approved, what code and data may be shared with them, how AI-assisted work must be reviewed, and who is accountable when AI output causes a problem. Review the policy every few months, because the tools change quickly.
Keep a Human Accountable for Every Merge
AI can review code, suggest fixes, and even approve its own pull requests if the pipeline allows it. The risk is that when something breaks in production, nobody owns the decision that let it through. “The AI approved it” is not an answer a client or an auditor will accept.
Every merge needs a named person who approved it and understands what it changes. AI review tools are still valuable as a first pass, catching style issues, missing tests, and obvious bugs so the human reviewer can focus on logic and design. But the final approval belongs to an engineer, and the merge history should show who it was.
Strengthen Tests Before Adding Coding Agents
Coding agents work by writing a change, running the tests, and fixing whatever fails. That loop only works if the tests actually catch mistakes. With a weak test suite, an agent can write broken code, see every test pass, and open a pull request that looks finished.
Before giving agents real tickets, check how much your tests can be trusted. Do they cover the most important user flows? Do they fail when the business logic is wrong, not just when the code crashes? Fill the biggest gaps first, ideally with tests written from the requirements. A strong test suite is what turns an agent from a risk into a reliable teammate.
Scan AI-Generated Code Like Any Unreviewed Code
AI-generated code often looks clean and confident, which makes it easy to trust. That trust is not yet earned. Veracode’s 2026 research found that leading AI models still introduce security flaws in a large share of coding tasks, and their security results have barely improved from the year before.
An AI-powered secure SDLC handles this with routine rather than suspicion. Run static analysis and dependency checks on every AI-assisted change, give the AI your secure coding rules as context, and keep production credentials out of reach of coding agents. Treat AI output like code from a new contractor: useful, often good, and always checked before it ships.
Give AI the Context Your Engineers Have
A new engineer is not productive on day one. They need to learn the codebase, the team’s conventions, and why certain decisions were made. AI tools face the same problem, except most teams never onboard them. The result is code that runs but doesn’t fit: the wrong naming style, a duplicated helper function, a pattern the team retired last year.
Start by writing down what your engineers already know and making it available to AI tools. Coding standards, architecture notes, approved libraries, and a few good examples from your own codebase all improve the output noticeably. The more an AI tool knows about how your team works, the less time engineers spend rewriting what it produces.
Measure Delivery Outcomes, Not Lines of Code
It’s tempting to judge AI by how much it produces: lines of code written, pull requests opened, tickets closed. Those numbers almost always go up, and they say very little. A team can double its code output and still ship slower if the extra code clogs review or breaks in production.
Measure what users and clients actually feel instead. Four delivery metrics work well: how long a change takes to reach production, how often you deploy, how often a release causes a failure, and how quickly you recover when it does. Record them before you roll out AI tools, then compare after a few months. If the numbers haven’t improved, the bottleneck is somewhere else.
Is Your Team Ready for AI-SDLC? A Quick Readiness Check
Your readiness for AI-SDLC depends less on which AI tools you choose than on how solid your delivery process already is. Answer the six questions below honestly. They take five minutes and show where AI will help and where it will make existing problems worse.
| Question | Ready if… | Not ready if… |
|---|---|---|
| Do you trust your test suite? | Tests catch most regressions before release | Bugs are mostly found by users |
| How fast is your CI pipeline? | Most builds finish in under 15 minutes | Builds take hours or fail at random |
| Who reviews code? | Reviewers have time set aside for it | Pull requests wait days for review |
| Is there an AI usage policy? | It is written, shared, and followed | Each developer picks their own tools |
| Is security scanning automatic? | Checks run on every merge | Scans happen only before major releases |
| Is engineering knowledge written down? | Standards and architecture notes are current | Key knowledge lives in a few people’s heads |
If you answered “not ready” three or more times, fix those foundations before scaling AI. Adding AI tools to a shaky process doesn’t fix it; it just exposes the weak points faster. If most answers fall in the “ready” column, you can move to AI-driven delivery with confidence, starting with the bottleneck that costs your team the most time.
How Kaopiz AI-SDLC Puts AI to Work With Humans in Control
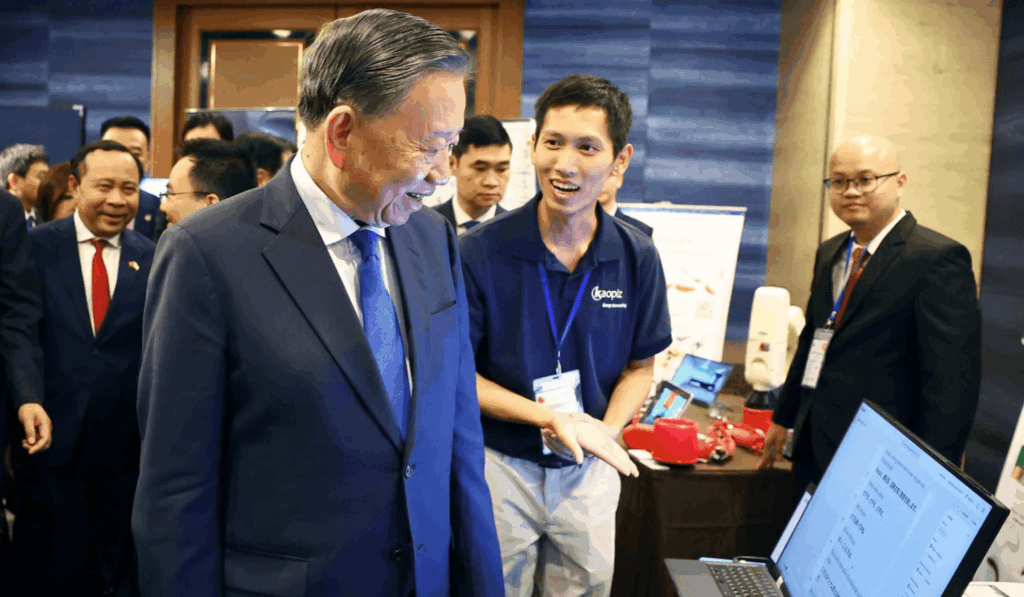
Kaopiz AI-SDLC is our own framework for running AI across the whole software lifecycle, from requirements to release, with an engineer approving every step. We demonstrated it live in Tokyo on November 9, 2026, at the Vietnam–Japan Public-Private Forum on Economic and Science-Technology Cooperation.
The framework grew out of our own work delivering AI development services. Founded in 2014, Kaopiz has nearly 1,000 staff and has delivered more than 1,000 projects for over 500 clients worldwide.
Five AI agents, called KARI, work from the same project data, keeping requirements, code, and tests consistent:
- KARI Writer drafts requirements and design documents.
- KARI Engineer supports coding.
- KARI Inspector supports testing and drafts test cases.
- KARI Manager supports release and project management.
- KARI Assistant answers questions about the project.
AI proposes, and people decide. Every phase has a mandatory Human Review Gate, so only work an engineer has approved moves forward. Every action is also logged for audit.
Security follows the standards of our clients, with six layers of protection, including an internal VPN, single sign-on, two-factor authentication, and separate data for each project. Clients can also switch AI models without changing their process.
Based on our internal estimates, the framework reduces effort from requirements to design by 30–50% and test design effort by up to 60%, depending on the project.
When comparing AI outsourcing partners in Singapore, ask whether AI sits inside a governed process or only on individual developers’ laptops.
Conclusion
AI-SDLC is less about adding AI tools and more about changing how a team works. AI can draft requirements, code, and tests in minutes, but real gains come only when review, testing, and governance keep pace. Teams that start with their biggest bottleneck, keep a human accountable for every decision, and measure delivery outcomes get faster releases without sacrificing quality.
If you’re still wondering what AI-SDLC would look like for your own projects, the readiness check above is a good place to start. When you’re ready to move further, talk to our team about bringing AI into your delivery process with clear controls and engineers in charge.
FAQs
- Is AI-SDLC the Same as the Lifecycle for Building AI Systems?
- No. AI-SDLC uses AI to build any kind of software, from a banking portal to a logistics app. The lifecycle for building AI systems covers data collection, model training, evaluation, and production monitoring, usually under the name MLOps. When people search for AI SDLC for software, they usually mean the first.
- How Could AI Help Optimize Software Performance During the SDLC?
- AI catches slow code before release and spots problems after it. During code review, it flags patterns that slow down under real load, such as a loop that queries the database once per item. In testing, it generates load tests from real traffic, and in production it alerts teams when a service starts to slow down.
- Does AI-SDLC Replace Agile or DevOps?
- No. AI-SDLC works inside Agile and DevOps rather than replacing them. Sprints, backlogs, and CI/CD pipelines stay the same. What changes is the work inside each step: AI drafts user stories, code, and tests, while the team reviews, adjusts, and approves them.
- Will AI Replace Developers in the SDLC?
- No, but the role is changing. Developers spend less time writing routine code and more time defining problems, reviewing AI output, making architecture decisions, and owning quality. Teams still need experienced engineers, because someone has to judge whether AI-generated work is correct, secure, and right for the business.
- What Tools Are Used in AI-SDLC?
- AI-SDLC tools fall into a few groups: coding assistants such as GitHub Copilot and Cursor, coding agents such as Claude Code and OpenAI Codex, AI code review tools, AI-powered testing tools, and AIOps platforms such as Datadog and Dynatrace for monitoring. Most teams combine several rather than relying on one.
Author
Leo Nguyen
Chief Executive Officer of Kaopiz Global
Table of Contents
Don’t miss what’s next!
Thank you! Your form has been submitted successfully.